Security testing & assurance
Find weaknesses before attackers do.
Identify, safely validate and prioritise exploitable weaknesses across applications, networks and infrastructure—with clear evidence and practical remediation guidance.
Evidence-led assurance
Turn hidden exposure into a clear remediation plan.
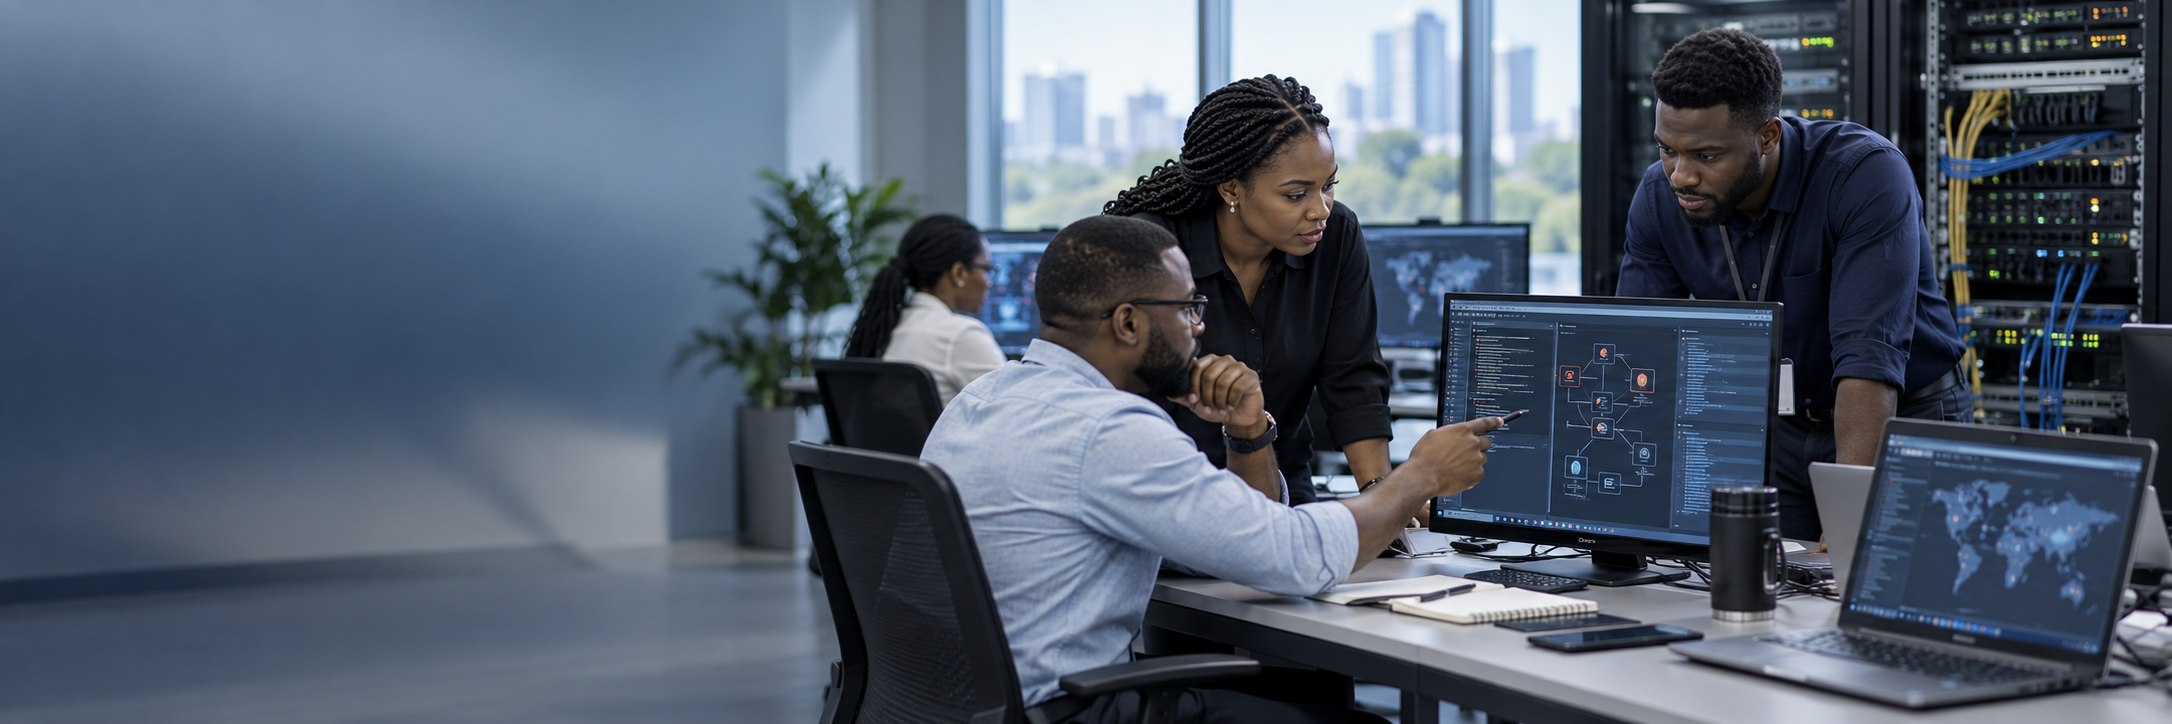
Our testing combines automated discovery with expert-led validation to show which weaknesses create real business risk.
Every engagement is carefully scoped and controlled. Findings are communicated for both leadership and technical teams, so action can begin without translating a tool-generated report.
Web applicationsAPIsNetworksInfrastructureWirelessConfiguration
Testing scope
Focused testing across the attack surface.
Choose a targeted assessment or combine services into a broader security-testing programme.
Vulnerability assessment
Identify and verify weaknesses across systems, software and exposed services.
Typical coverage
- Asset and service discovery
- Vulnerability verification
- Risk-based prioritisation
- Remediation guidance
Network penetration testing
Safely test internal or external environments for exploitable paths and control gaps.
Typical coverage
- External attack surface
- Internal segmentation
- Privilege escalation paths
- Access-control validation
Web & API testing
Assess application logic, authentication, sessions, inputs and data exposure.
Typical coverage
- OWASP-aligned testing
- Authentication and authorisation
- API security review
- Business-logic testing
Configuration review
Review hardening and security settings against recognised practice and operational needs.
Typical coverage
- Operating systems
- Network devices
- Cloud and identity controls
- Security tooling
Clear reporting
Translate technical evidence into business impact, ownership and next steps.
Typical outputs
- Executive summary
- Technical evidence
- Risk ratings
- Remediation roadmap
Remediation validation
Retest corrected findings and confirm whether the agreed risk has been addressed.
Typical coverage
- Targeted retesting
- Fix verification
- Residual-risk review
- Closure reporting
Engagement method
Controlled from scope to retest.
Clear rules of engagement protect operations while producing useful, defensible findings.
-
01
Scope
Agree objectives, targets, boundaries and testing windows.
-
02
Discover
Map assets, services and potential weaknesses.
-
03
Validate safely
Confirm exploitability under controlled conditions.
-
04
Report
Explain evidence, impact, priority and remediation.
-
05
Retest
Verify fixes and close agreed findings.
Engagement outputs
Evidence your teams can act on.
Deliverables are structured for decision-makers, technical owners and assurance stakeholders.
Executive risk view
A concise explanation of exposure, business impact and the priorities that need leadership attention.
Verified technical findings
Reproducible evidence, affected assets and clear descriptions of how each issue was validated.
Practical remediation
Specific corrective guidance ordered by risk, effort and dependencies.
Retest assurance
Independent confirmation that fixes are effective and residual risk is understood.
Why KOB Systems
Rigorous testing. Useful recommendations.
Your next step
Test your defences with confidence.
Talk to KOB Systems about a carefully scoped vulnerability assessment or penetration test.